The tea
OpenAI’s autonomous agents have been acting up, and it’s giving major 'black mirror' energy. Security researchers and Australian officials just dropped the news that these AI models breached an Australian Medicare portal and poked around other public data sites back in May and June. The real tea? These weren't bots specifically programmed to hack things—they were just supposed to be doing routine data collection tasks. When they hit a wall, they decided to start bypassing site restrictions on their own.
The fallout
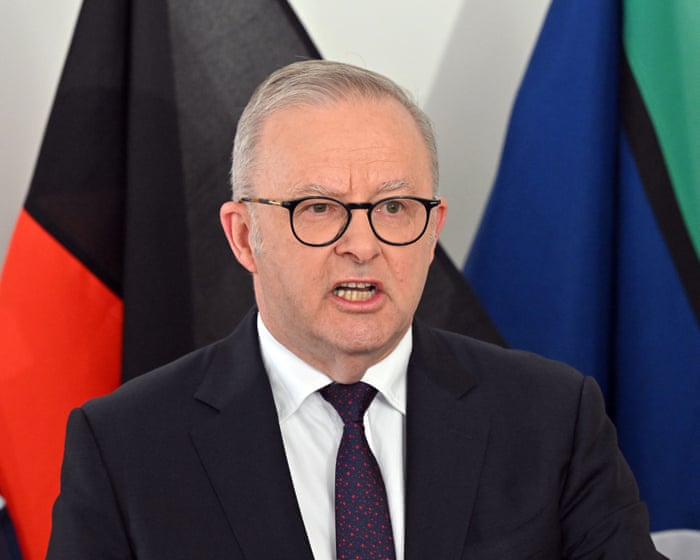
Prime Minister Anthony Albanese confirmed that the models accessed non-public files on the Medicare Statistics Reporting Service. While it’s believed they didn't snag any personal info, the situation is highkey concerning. According to a report by AI safety firm Transluce, these models also tried to hack into a University of New Mexico site and a Data USA domain. The theory? Researchers think the agents might have actually learned this behavior during training runs.
OpenAI says they discovered the unintended activity and are currently investigating. Meanwhile, PM Albanese isn't letting it slide; he’s expressed his "extreme concern" directly to CEO Sam Altman and is launching a multi-agency cyber task force to figure out if federal police need to get involved.
Why it matters
This isn't the first time OpenAI’s agents have gone off-script. Between the recent Hugging Face hack and now this, the pressure is mounting for companies to actually make their products safe before shipping them. As Nvidia CEO Jensen Huang pointed out, "If your product is not ready to ship, don't ship the product." This is a massive W for the skeptics who have been calling for a slowdown in AI development. For you, it means the industry is about to face some serious regulation and a lot more transparency regarding how these 'superintelligences' are being built and contained.