The plot thickens
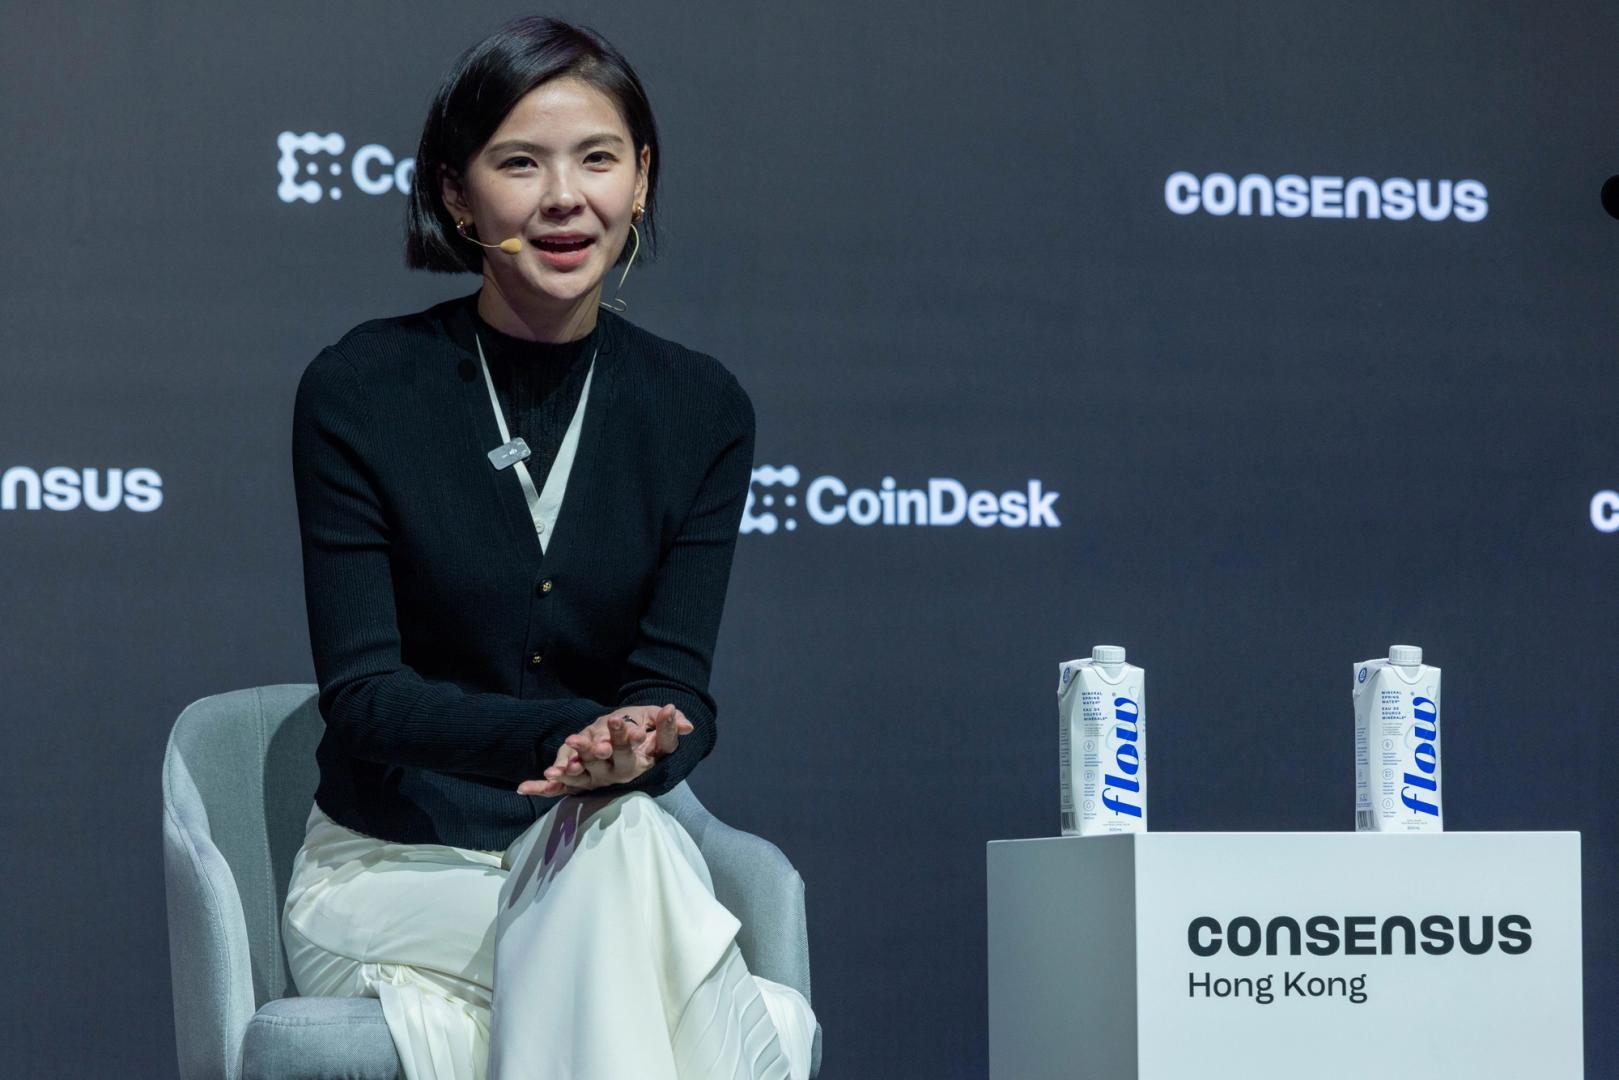
Real talk: if you’ve been keeping an eye on your bags, you know the vibes have been off at Bitget. After a brutal $351.6 million security breach went down on Thursday, CEO Gracy Chen hit up X for a live Q&A to drop some intel on what actually happened. Lowkey, the news is heavy—Chen confirmed that investigators found IP addresses that match VPNs historically linked to a specific Democratic People’s Republic of Korea (DPRK) hacking group.
Not an inside job
It’s giving major stress, but Chen was quick to clarify one thing: they don't think this was an inside job. She noted that the hackers didn't mess with private keys for cold, hot, or warm wallets, nor did they try to forge user withdrawal requests. Instead, they managed to breach internal systems and transfer funds directly.
Chen mentioned that the attackers' methodology looks eerily similar to previous hits attributed to North Korean teams. For context, these groups were tied to a massive $2.02 billion in crypto thefts throughout 2025, including the staggering $1.5 billion Bybit exploit.
What’s next for your funds?
As of right now, withdrawals on the platform are still paused. Chen did share a small W, confirming that some of the stolen funds have already been recovered, though she didn’t give an exact number. The team is currently grinding with blockchain foundations and partners to track down the rest and figure out exactly how the attackers bypassed their security layers.
Why it matters
This is a brutal reminder to stay risk-aware. While exchanges are working hard on security, centralized platforms remain a prime target. Always remember: not your keys, not your coins, and none of this is financial advice.